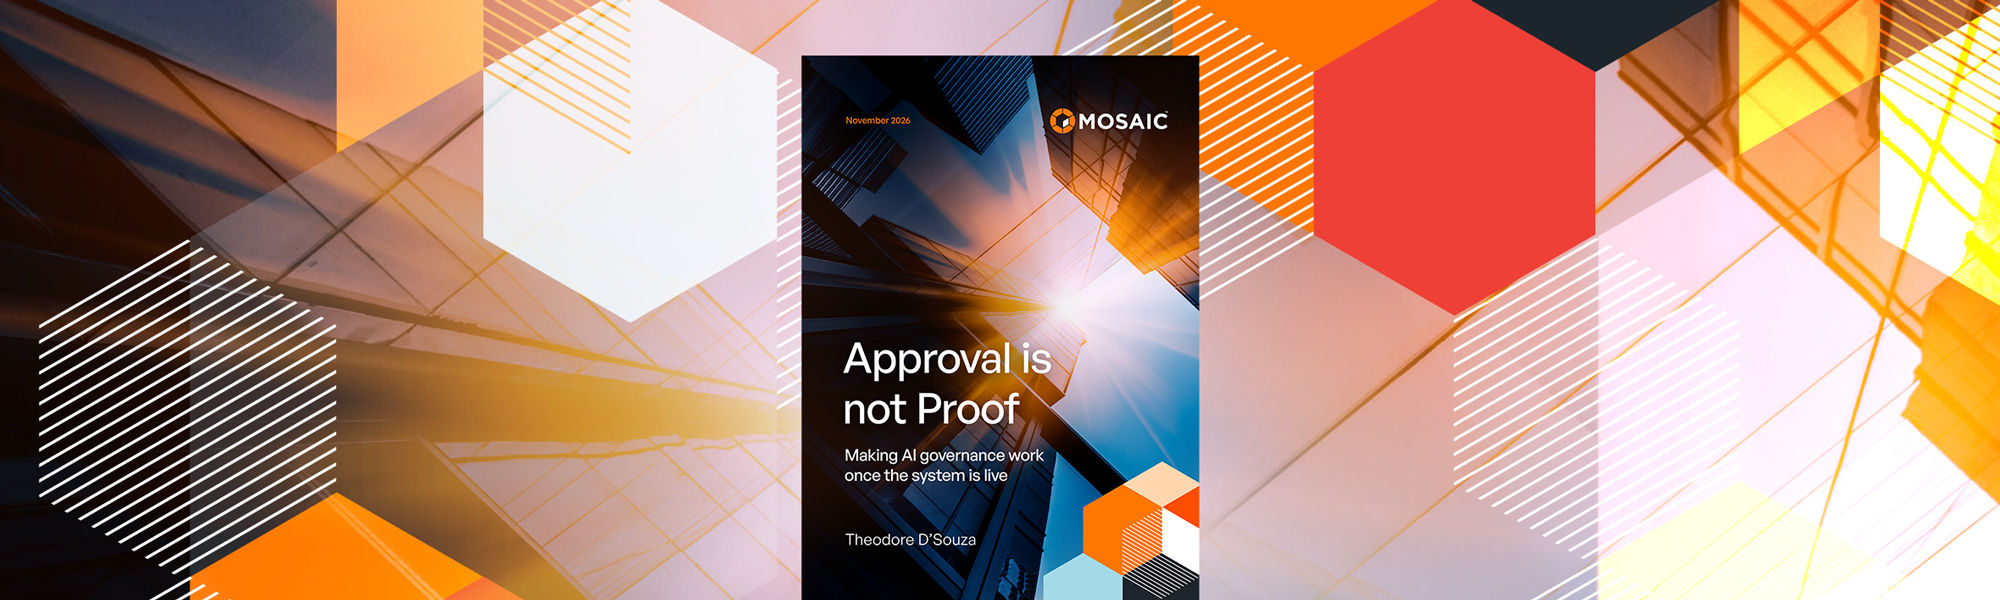
Enter your details to read the white paper.
Most New Zealand financial services organisations now have an AI policy, a named owner and an approval process for new use cases. That is real progress. But having these structures in place raises a more practical question:
If this system produced a harmful output tomorrow, who would notice first, who could act, and what would happen next?
Most people who try this exercise can name who would notice, and it is usually someone on the frontline. Far fewer can name who has the authority to act.
This paper draws on master’s-level study of AI governance, power and organisational change.
Its central lesson is that approval records that governance happened once. It does not show whether an organisation can detect, challenge and stop harm once a system is in daily use. For financial services, where AI adoption is moving quickly alongside conduct, privacy and risk expectations, that is where much of the real exposure sits, and where governance and change management need to work together.
The paper sets out how approved systems drift, why the burden tends to fall on frontline staff, what an organisation must be able to say about its AI, and how to test whether governance is still alive six months after go-live. It aligns with how Mosaic works across Advice, Design, Execution and Governance.

By Theo D'Souza | Senior Change Consultant, Mosaic
Theo leads our Change Management Service Line working with our clients to meet their transformation goals by focusing on people-first change delivery. He is currently studying a Masters in Applied Artificial Intelligence and is actively applying the skills learnt to the Change Management Service Line. Generative AI is here to stay and Theo is interested in understanding how this continues to change the way your people and your organisation implement, evolve and work with these tools to get the best out of them.

Enter your details to read the white paper.
Most New Zealand financial services organisations now have an AI policy, a named owner and an approval process for new use cases. That is real progress. But having these structures in place raises a more practical question:
If this system produced a harmful output tomorrow, who would notice first, who could act, and what would happen next?
Most people who try this exercise can name who would notice, and it is usually someone on the frontline. Far fewer can name who has the authority to act.
This paper draws on master’s-level study of AI governance, power and organisational change.
Its central lesson is that approval records that governance happened once. It does not show whether an organisation can detect, challenge and stop harm once a system is in daily use. For financial services, where AI adoption is moving quickly alongside conduct, privacy and risk expectations, that is where much of the real exposure sits, and where governance and change management need to work together.
The paper sets out how approved systems drift, why the burden tends to fall on frontline staff, what an organisation must be able to say about its AI, and how to test whether governance is still alive six months after go-live. It aligns with how Mosaic works across Advice, Design, Execution and Governance.
By Theo D'Souza | Senior Change Consultant, Mosaic
Theo leads our Change Management Service Line working with our clients to meet their transformation goals by focusing on people-first change delivery. He is currently studying a Masters in Applied Artificial Intelligence and is actively applying the skills learnt to the Change Management Service Line. Generative AI is here to stay and Theo is interested in understanding how this continues to change the way your people and your organisation implement, evolve and work with these tools to get the best out of them.